ความปลอดภัยในโรงงานสมัยใหม่ไม่ใช่แค่ "ติดกล้องวงจรปิด" — ครอบคลุม คน, ทรัพย์สิน, ข้อมูล, ระบบควบคุม บทความนี้สรุประบบความปลอดภัยที่โรงงานยุค Industry 4.0 ต้องมี
ระดับของความปลอดภัยในโรงงาน
┌─────────────────────────────────────┐
│ Layer 4: Operational Safety         │  ← PPE, ergonomics, training
├─────────────────────────────────────┤
│ Layer 3: Cyber Security             │  ← Network, OT, ransomware
├─────────────────────────────────────┤
│ Layer 2: Access Control             │  ← Door, restricted zone
├─────────────────────────────────────┤
│ Layer 1: Physical Surveillance      │  ← CCTV, perimeter
└─────────────────────────────────────┘
แต่ละ layer ต้องการ technology ต่างกัน
Layer 1: CCTV + AI Analytics
ยุคก่อน CCTV ใช้แค่ "ดูย้อนหลังหลังเหตุการณ์" — ปัจจุบัน AI วิเคราะห์ real-time เพื่อแจ้งเตือนทันที
Use Cases ที่ AI Analytics ทำได้:
1. Intrusion Detection
- ตรวจคนเข้า restricted zone
- กลางคืน → alert ทันที
- Reduce false alarm 90% (เทียบกับ motion sensor)
2. PPE Detection (ดู Object Detection)
- ตรวจหมวกนิรภัย, เสื้อสะท้อนแสง
- Buzzer + LINE alert
- ลดอุบัติเหตุ 40-60%
3. Loitering Detection
- คนยืนแช่ในจุดอันตราย > 30 วินาที
- ตู้ ATM, electrical panel, chemical storage
4. Fall Detection
- ตรวจจับคนล้มในโรงงาน
- Critical สำหรับ lone worker
5. Crowd Density
- นับคนใน canteen, locker
- ปรับตาม COVID, fire safety
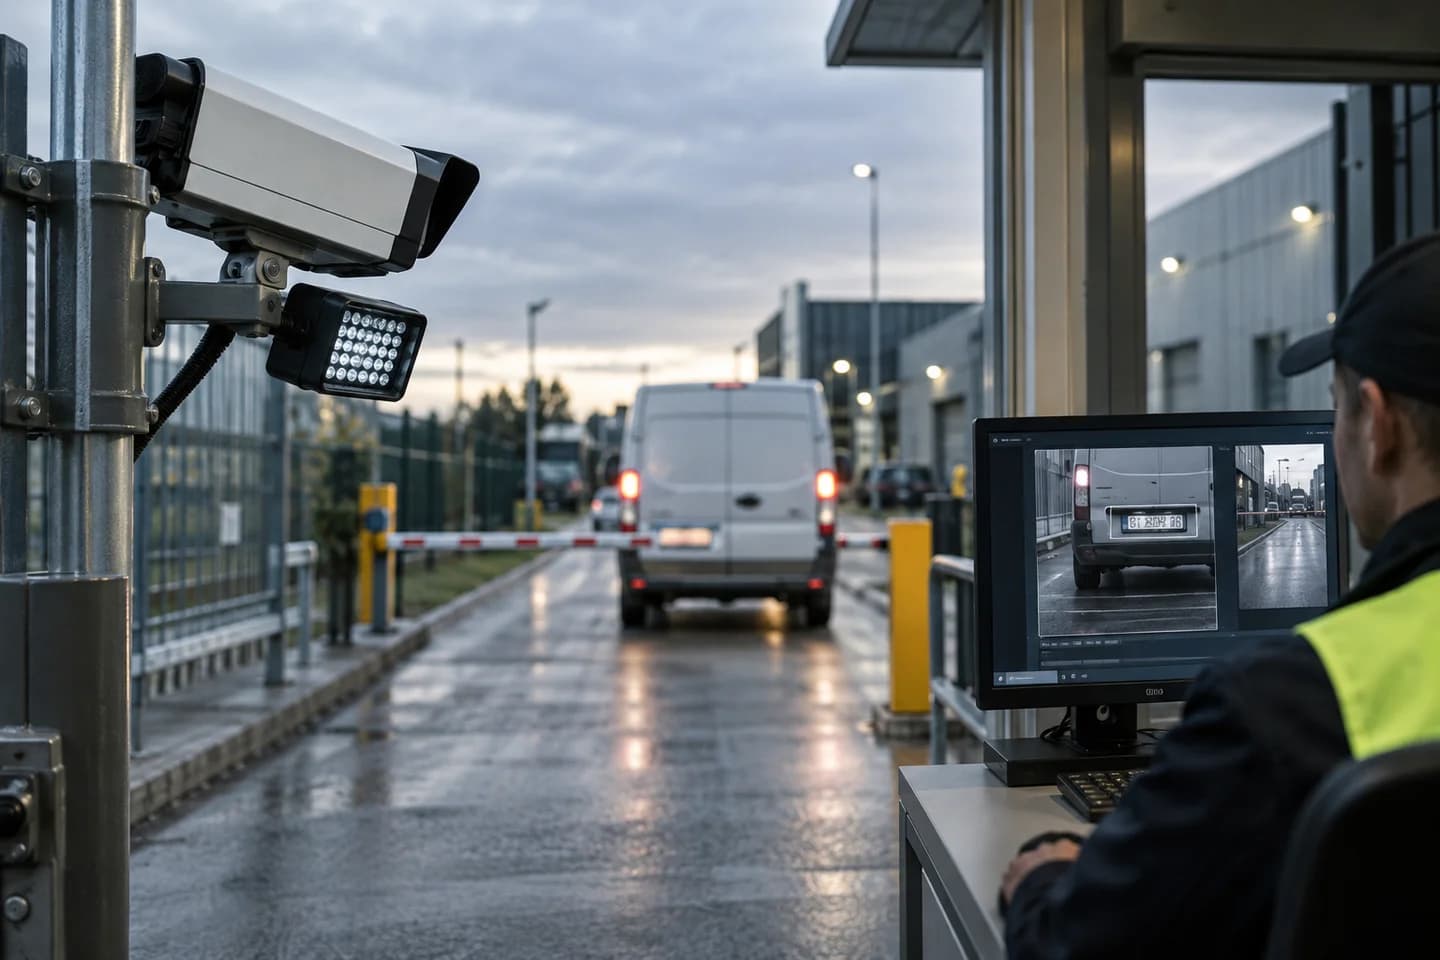
6. Vehicle Recognition (LPR)
- License Plate Recognition ที่ประตู
- Auto-open สำหรับรถขึ้นทะเบียน
- Log ทุกเข้าออก
Hardware ที่แนะนำ:
| Camera | ราคา | ใช้ตรงไหน | |--------|------|-----------| | IP Bullet 4MP | 3,000-8,000 | ทั่วไป indoor | | PTZ 4MP | 15,000-40,000 | Perimeter, large area | | Thermal | 60,000-200,000 | Fire, complete darkness | | Panoramic 360° | 20,000-50,000 | Warehouse, parking |
NVR / Recording
- Edge NVR (Hikvision, Dahua) — 8 channels 30,000-50,000
- Server-based — ขยายได้ไม่จำกัด, ต้อง IT
- Cloud VMS — ไม่ต้อง maintain, monthly fee
AI Analytics Platform:
- Hikvision/Dahua AI series — built-in, 1-2 features
- NVIDIA Metropolis — flexible, build custom
- Custom (YOLO + DeepStream) — ดูที่ Object Detection
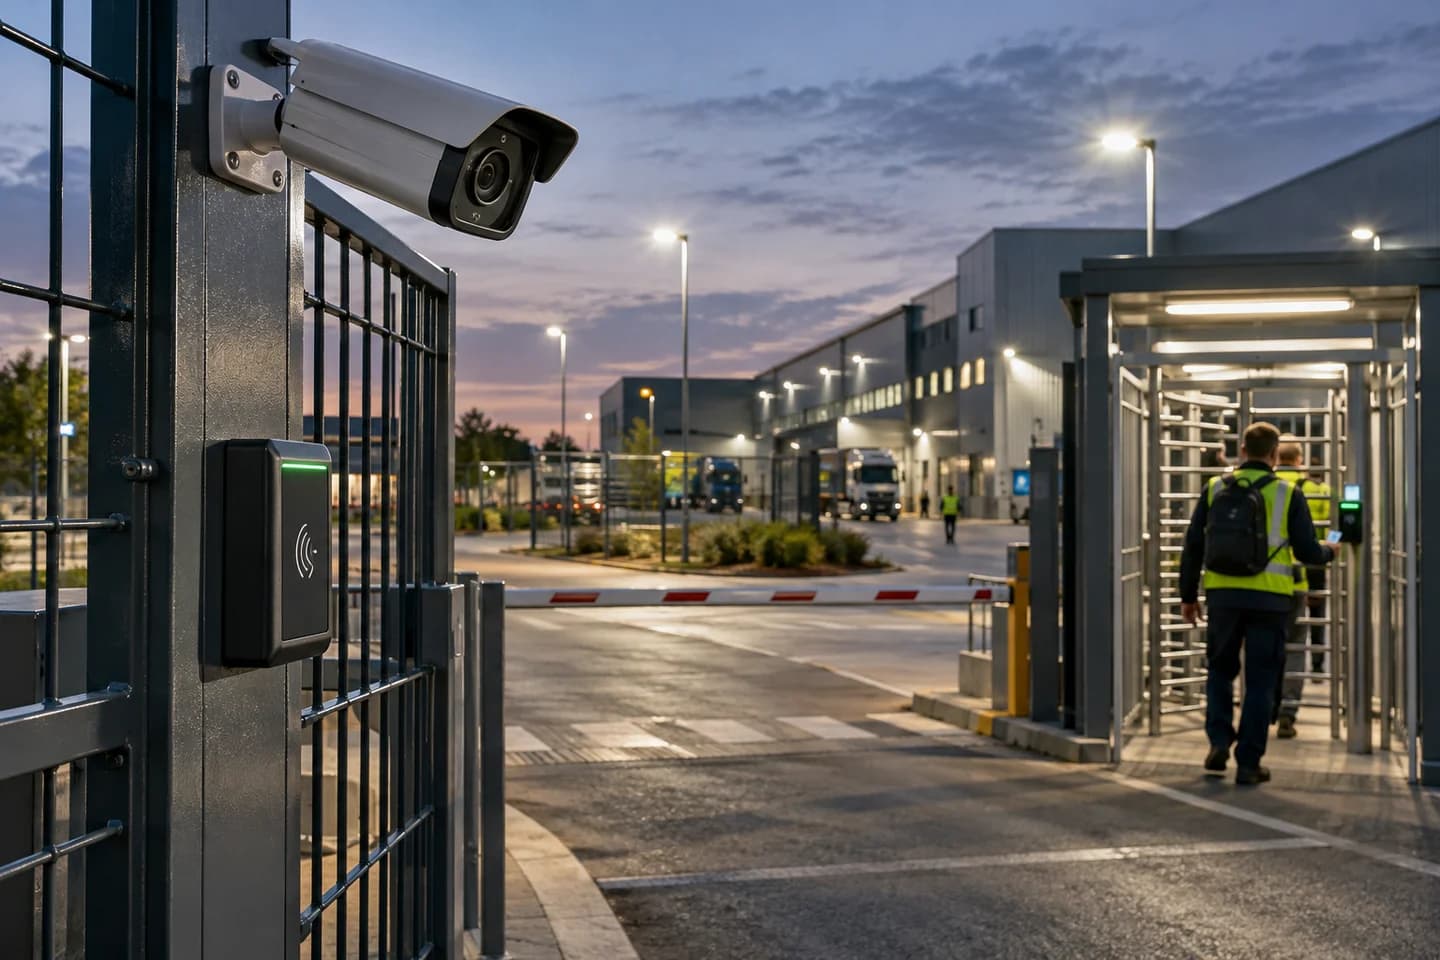
Layer 2: Access Control System
Technology ที่ใช้กัน:
1. Card-based
- Mifare/HID — มาตรฐาน, ราคาถูก
- Long-range UHF — ผ่านได้ขณะเดินเฉยๆ
2. Biometric
- Fingerprint — แม่นยำ, ราคาถูก แต่ติดเชื้อ
- Face Recognition — Touch-less, AI ทำได้แม่น 99.5%
- Palm Vein — แม่นยำสุด ปลอมยาก
3. Mobile-based
- Bluetooth (BLE) — ใช้มือถือเปิดประตู
- NFC — Tap-to-enter
Architecture แนะนำ
[Reader] → [Door Controller] → [Access Server] → [HR/AD]
                                       ↓
                                [Audit Log]
                                       ↓
                              [Alert + Reports]
Best practices:
- Multi-factor สำหรับ critical zone (Card + Face)
- Time-based access — พนักงานกะดึกเข้าได้แค่ช่วงกะ
- Anti-passback — ป้องกันส่งบัตรกัน
- Integration with HR — ลาออกแล้วบัตรปิดทันที
ROI:
- ลดต้นทุน security guard 30-50%
- Audit trail สมบูรณ์ (compliance)
- ลดการขโมย/ไม่ได้ตั้งใจ 90%
Layer 3: Cyber Security (สำคัญมากในยุค Industry 4.0)
โรงงานที่เชื่อมต่อ IT/OT (Operational Technology) มี attack surface ใหญ่ขึ้นมาก ransomware ที่โจมตี SCADA/PLC ทำโรงงานหยุดได้หลายวัน
Threat Landscape:
1. Ransomware
- โจมตี Windows server → encrypt files
- Spreading ผ่าน SMB, RDP
- Cost: หยุดผลิต + ค่าไถ่ + recovery
2. ICS/SCADA Attack
- Stuxnet-like — เข้าถึง PLC โดยตรง
- เปลี่ยน setpoint, สั่งหยุด/เร่ง
- อันตรายต่อชีวิต
3. Supply Chain Attack
- Compromise vendor remote access
- Backdoor ใน firmware update
4. Insider Threat
- พนักงานเก่ากลับมาทำลาย
- USB ผูกข้อมูลออก
มาตรการที่ต้องมี:
1. Network Segmentation
[Internet]
    ↓
[Firewall + IDS]
    ↓
[Corporate IT Network]  ← ERP, Email, Office
    ↓
[DMZ + Data Diode]  ← One-way data flow
    ↓
[OT Network]  ← MES, SCADA, Historian
    ↓
[Field Devices]  ← PLC, RTU, sensors
2. Patching Strategy
- IT: patch ทุกเดือน
- OT: patch ผ่าน test environment ก่อน → schedule maintenance
3. Backup + Disaster Recovery
- 3-2-1 Rule: 3 copies, 2 media, 1 offsite
- Test restore ทุก quarter
- Air-gapped backup สำหรับ critical system
- พิจารณา Cloud VPS เป็น offsite backup ที่ใช้งานง่ายและประหยัด
4. Endpoint Protection
- Antivirus + EDR บน Windows
- USB control (whitelist mode)
- Application whitelisting บน HMI
Email Server บริษัท ที่ดีต้องมี Anti-Phishing + DLP + SPF/DKIM/DMARC ครบ — เพราะ 90% ของ ransomware เข้าทาง email
5. Monitoring + Logging
- SIEM รวม log จาก IT + OT
- Anomaly detection (ดู AI)
- 24/7 SOC (in-house หรือ MSSP)
6. Identity & Access
- MFA สำหรับ remote access
- Privileged Access Management (PAM)
- Service account audit
Compliance ที่เกี่ยวข้อง:
- IEC 62443 — ICS Security (มาตรฐานหลัก)
- NIST Cyber Security Framework
- ISO 27001
- PDPA (สำหรับข้อมูลส่วนบุคคล)
Layer 4: Operational Safety
Physical Safety:
- E-Stop button ทุก station
- Light curtain ป้องกันคนเข้าใกล้เครื่อง
- Lockout/Tagout (LOTO) — ปลอดภัยตอน maintenance
- Gas detector ใน confined space
Environmental Monitoring:
- Temperature, humidity
- Air quality (CO, VOC)
- Noise level
- Lighting (lux meter)
Lone Worker Safety:
- Smart watch + man-down detection
- Periodic check-in via mobile app
- Alert ถ้าไม่ตอบ > 15 นาที
Architecture แบบรวม (Unified Security)
[CCTV] [Access Control] [Cyber] [Safety Sensors]
       ↓         ↓          ↓          ↓
        [Unified Security Platform]
                  ↓
        [Alert + Dashboard + Reports]
                  ↓
        [SOC + Mobile App]
ระบบที่ดีต้อง correlate events ข้าม layer:
- Alert "Door forced + Camera shows intruder + No badge scan"
- ไม่ใช่ alert แยกกัน 3 ที่
งบประมาณตัวอย่าง (โรงงานขนาดกลาง 10,000 ตร.ม.)
| Layer | รายการ | บาท | |-------|-------|-----| | CCTV + AI | 30 cameras + NVR + AI analytics | 1,200,000 | | Access | 10 doors + biometric + server | 600,000 | | Cyber | Firewall + EDR + backup | 800,000 | | Safety | E-stop, gas detector, monitoring | 400,000 | | Integration + training | | 500,000 | | รวม | | 3,500,000 |
ROI:
- ลด guard 30%
- ลด theft + damage 80%
- หลีกเลี่ยง 1 incident ransomware (cost ~ 5-50M)
- Payback: 18-30 เดือน
ความเสี่ยงที่ต้องระวัง
❌ ติดตั้งแล้วไม่ดู
ระบบ security ที่ไม่มีคนดู = ไม่มีระบบ แก้: SOC team หรือ outsource MSSP
❌ Cyber + Physical แยกกัน
แก้: Converged security operation
❌ Privacy จาก facial recognition
แก้: Comply กับ PDPA, ขอความยินยอม
❌ อัปเดตไม่สม่ำเสมอ
แก้: Patch management policy + responsible person
สรุป
ความปลอดภัยโรงงานยุคใหม่ต้องเป็น integrated system — Physical + Cyber + Safety เชื่อมกัน
เริ่มจาก threat assessment → ทำ priority → ลงทุนตามนั้น อย่าซื้อของหรูๆ มาแล้วไม่ใช้
อ่านต่อ
- Object Detection ในโรงงาน — รากฐานของ AI surveillance
- เริ่มต้น IoT ในโรงงาน — IoT security ก็ต้องใส่ใจ
- ระบบบันทึกข้อมูลการผลิต — Data layer ที่ปลอดภัย
หากต้องการประเมินความเสี่ยงด้านความปลอดภัยในโรงงาน ไนท์เดย์ เทคโนโลยี มีทีม Security Architect ที่ทำงานออกแบบทั้ง physical และ cyber security สำหรับโรงงาน — ติดต่อเรา เพื่อพูดคุยรายละเอียด